Your data. Our highest priority.
Data security and compliance for translation and interpreting
From M&A disclosures to clinical trial data, your most sensitive content is protected across the whole language lifecycle: an ISO/IEC 27001:2022 certified environment with SOC 2 Type II audited controls.
Book a security walkthrough (opens Zoho Bookings in a new tab)Request security documentation
- UploadThrough our client portal over TLS 1.2+, never open email
- StorageEncrypted at rest with AES-256, in the region you choose
- AssignmentOnly the background-checked linguists on your project, under NDA
- DeliveryBack through the portal, with multi-factor authentication
- PurgeSource files removed on your retention schedule
Defense-in-depth infrastructure
A layered security strategy that lowers risk at every point: technology, process, and people. Our controls have been refined through years of federal review.
-
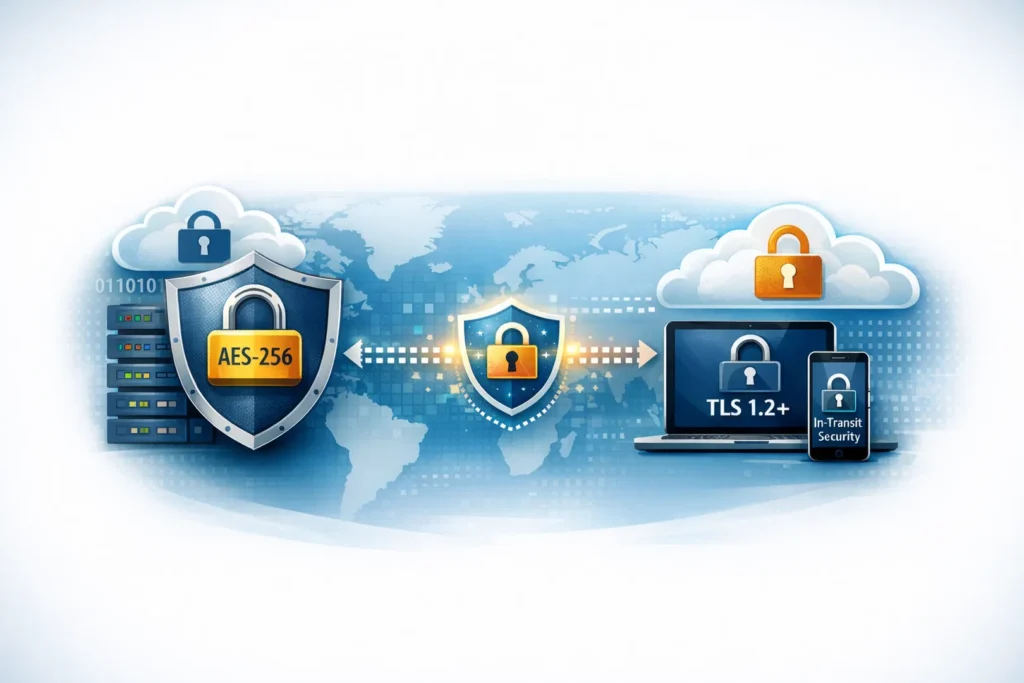
In transit and at rest
Data encryption
All data is protected with AES-256 encryption at rest and TLS 1.2+ in transit. Your files never sit on unsecured local machines or public cloud folders.
-
Air-gapped workflows
Secure client portal
Our portal removes the risk of sharing files by email. Access requires multi-factor authentication, and enterprise clients can restrict access to approved IP addresses.
-
Data minimization
Zero-knowledge architecture
Strict retention policies apply to every project. Once a project is delivered, source files are purged from our active processing environment on the schedule your compliance requirements set.
Global compliance readiness
The frameworks your security and privacy reviewers ask about, and where we stand on each.
| Framework | Our status | Focus area |
|---|---|---|
| ISO/IEC 27001:2022 | Certified | Information security management system, independently audited |
| SOC 2 Type II | Audited controls | Controls for security, availability, and privacy |
| HIPAA | BAA signed | Safeguards for protected health information (PHI), with a Business Associate Agreement for covered entities |
| GDPR | Compliant workflows | Privacy of EU residents and data subjects |
| CCPA | Compliant workflows | Consumer data rights for California residents |
Vetted personnel. Ironclad NDAs.
Technology is only as secure as the people who operate it. Every person who touches your content is screened, bound by confidentiality, and limited to what the job requires.
Background checks
Every linguist and project manager passes background screening before working on client content.
Tiered access
Linguists see only the content assigned to them, never your full file set or internal directories.
Confidentiality agreements
Every linguist signs a confidentiality agreement before receiving any client content.
Cleared linguists
For federal and high-security commercial projects, we can provide top secret cleared linguists.
Localized data hosting
To meet strict jurisdictional requirements, we offer regional data hosting. If your compliance rules require data to stay in the United States, the European Union, or specific APAC regions, we configure your workspace to meet local data sovereignty laws.
- United StatesFor federal, state, and U.S. regulated work
- European UnionFor GDPR data residency requirements
- Asia-PacificFor specific APAC jurisdictions
Put our security to the test
Our Security Office is ready to complete your vendor risk assessment or provide a live walkthrough of our encryption protocols.
Request an audit walkthrough (opens Zoho Bookings in a new tab)Contact security and compliance
- Your vendor security questionnaire, completed by our team
- A live walkthrough of our portal and encryption
- Copies of our ISO certificates
- Confidentiality agreements signed before any files move
FAQ
Data security, answered
Don’t see your question? A language specialist can answer it in one call.
Talk to a specialist
Get a straight answer
Tell us what you need translated or interpreted, and we’ll scope it with you.
Meet one-on-one with a language services expert, at a time that suits you.
How do you keep translation files secure?
Files move only through our encrypted client portal, never open email, with AES-256 encryption at rest and TLS 1.2+ in transit. Access requires multi-factor authentication and is limited to the background-checked linguists assigned to your project, all under confidentiality agreements.
Is Translation Excellence ISO 27001 certified?
Yes. Our information security management system is certified to ISO/IEC 27001:2022 and independently audited. Copies of our certificates are available for vendor reviews.
Do you have SOC 2 Type II?
Yes. Our controls for security, availability, and privacy are audited under SOC 2 Type II. SOC 2 is an audit report rather than a certification; contact us to discuss access for your vendor review.
Can you translate content that contains protected health information?
Yes. We sign a Business Associate Agreement, and protected health information is handled under our HIPAA compliance program, through the encrypted portal, by linguists bound by confidentiality, and deleted on the retention schedule you set.
Can our data stay in the United States or the European Union?
Yes. We offer regional data hosting in the United States, the European Union, and specific APAC regions, and configure your workspace to meet the data residency rules that apply to you.
Will you complete our vendor security questionnaire?
Yes. Our Security Office completes vendor security questionnaires and risk assessments, and can walk your reviewers through our portal and encryption live. Email info@translationexcellence.com or book a meeting.
Tell us what’s at stake. We’ll show you how we’d handle it.
Send your files or describe your event. A language specialist replies with a fixed quote and a delivery date, with no obligation.
Prefer to call? 720-325-0459